How Consent Works
This page explains the step-by-step consent process, what gets blocked before consent, and the security measures protecting the flow.
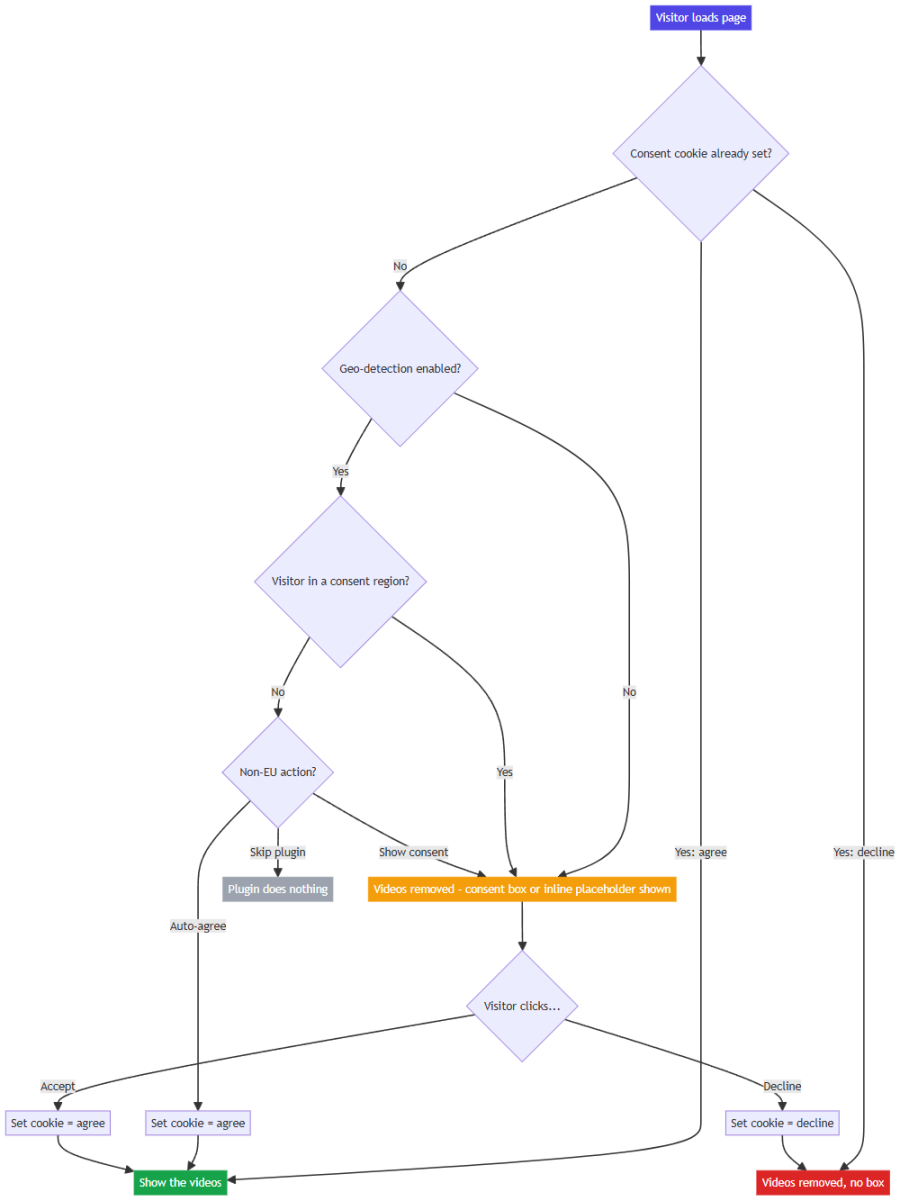
Consent Flow
What Gets Blocked
Before the visitor makes a consent decision, the plugin removes every detected piece of YouTube code from the page before it is sent:
- YouTube iframes (both
youtube.com/embedandyoutube-nocookie.com/embed) - The IFrame API script (
youtube.com/iframe_api), so no player JavaScript loads - Extension and page-builder markup: Smart Slider 3 video layers, the YouTube Gallery player script, oEmbed links and entity-encoded iframes
So the browser makes no request to YouTube, receives no YouTube cookie, and sends nothing to Google for the detected videos.
Two exceptions you control:
- YouTube thumbnail placeholder mode (opt-in) loads poster images from
img.youtube.combefore consent, which sends the visitor's IP address to Google. Every other placeholder mode keeps images on your server. See Placeholder Images. - Geo-detection (off by default): when it is on, visitors outside your consent regions are auto-accepted by default. See Geo-Detection.
Videos the plugin does not detect (for example a player built by JavaScript after the page loads) are not blocked. Use Debug Mode to check your pages.
After Consent
Accept (Load YouTube)
- The consent cookie
sly-consentis set toagree - On the next page load (and all subsequent loads while the cookie is valid), the original YouTube code is left untouched
- Videos play normally
Decline (Do not load videos, or the × close button)
- The consent cookie
sly-consentis set todecline - YouTube code continues to be stripped from the HTML on every page load
- The consent box is not shown again until the cookie expires
Security Features
CSRF Protection
Every consent form submission includes a Joomla CSRF token. The plugin validates this token before setting the consent cookie. This prevents cross-site request forgery attacks that could set consent on behalf of a visitor.
Secure Cookie Flags
The consent cookie is set with:
- HttpOnly — Cannot be read or modified by JavaScript, preventing XSS-based cookie theft
- Secure — Only transmitted over HTTPS (when Force HTTPS is set to Entire Site)
- SameSite=Lax — The cookie is not sent with cross-site requests, preventing CSRF via third-party sites
Input Validation
- The consent value is strictly validated to only accept
agreeordecline - All user-facing text (headline, consent text, button labels) is escaped with
htmlspecialchars - A malformed Custom Regex Pattern fails silently rather than breaking the page
Revoking Consent
There is no built-in revoke button. Visitors can revoke consent by:
- Clearing their browser cookies (the
sly-consentcookie specifically, or all cookies) - Waiting for the cookie to expire (if set to a day-based lifetime)
Once the cookie is gone, the consent dialog appears again on the next visit.